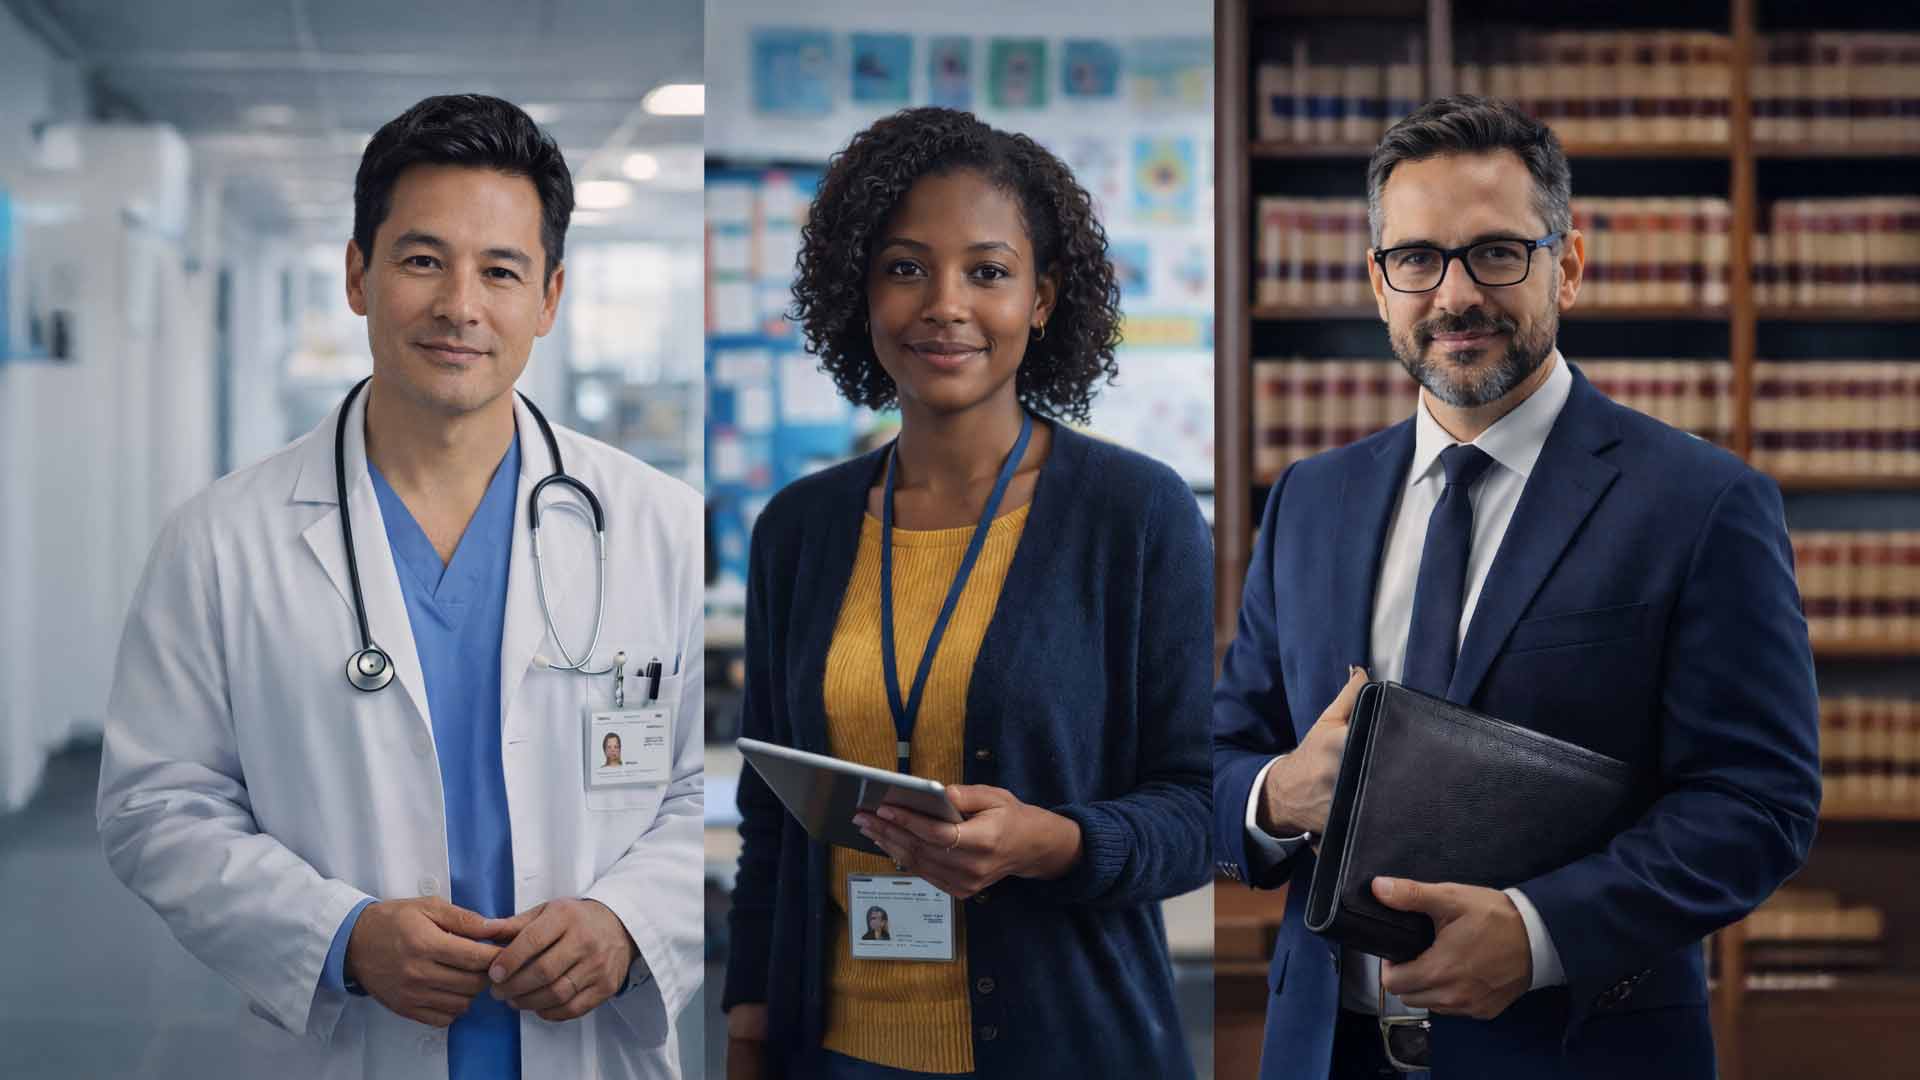
If your organization operates in healthcare, education, or legal services, you already know the stakes are different. You're not just managing technology — you're managing trust, privacy, and legal accountability. Patient records, student data, and confidential legal files must stay protected, accessible, and properly handled every single day.
IT support in these environments goes far beyond fixing a broken printer or resetting a password. It has to support compliance requirements, protect sensitive information from increasingly sophisticated threats, and reduce the very real risk of regulatory penalties. A single oversight can trigger audits, fines, reputational damage, or worse — interruptions to care, learning, or legal services that people depend on.
And here's the thing most organizations get wrong: compliance isn't the obstacle. It's the strategy. As Forbes noted in a 2026 analysis of regulated industries, the companies struggling most with compliance aren't being held back by regulations — they're being held back by how they think about them. When you start treating IT compliance as a competitive advantage rather than a burden, your entire approach to technology support changes.
This article walks through the best practices for IT support in regulated industries, what makes these environments uniquely demanding, and how a well-structured managed IT approach can help you stay protected, efficient, and audit-ready.
What Makes Healthcare, Education, and Legal IT Environments Unique?
These three industries share more than you might expect. They all manage large volumes of sensitive data. They all face strict rules about who can access that information and how it must be protected. And they all rely on technology to deliver essential services where downtime isn't just inconvenient — it's damaging.
- Healthcare: Downtime can delay patient care, disrupt clinical workflows, and compromise outcomes.
- Education: System failures can interrupt instruction, block access to records, and disrupt student services.
- Legal: A security breach can compromise attorney-client privilege, expose case files, and create serious ethical and contractual liability.
These realities demand a higher standard of IT support — one built around security, visibility, consistency, and documentation.
Regulatory Pressures That Shape IT Support
Each industry operates under its own regulatory framework, but the core expectations overlap significantly.
- Healthcare organizations must follow HIPAA rules governing patient data privacy, access controls, breach notification, and audit trails.
- Educational institutions must comply with FERPA requirements that protect student records and restrict who can access personal information.
- Legal organizations must uphold confidentiality obligations and data protection standards tied to ethical rules, bar requirements, and contractual responsibilities.
What all three share: control access, protect data, document processes, and respond effectively to incidents. IT support sits at the center of all of it.
Best Practice 1: Proactive Monitoring and Maintenance
Reactive IT support creates risk in regulated environments. Waiting for systems to fail — or for a security alert to fire — significantly increases the chance of compliance violations and data exposure.
Best-in-class IT support for regulated industries includes continuous monitoring of systems, networks, endpoints, and security events. Issues are caught early, before they disrupt operations or compromise protected data.
Proactive maintenance also means updates, patches, and performance adjustments happen on a predictable schedule. Systems don't drift out of compliance because patches were skipped or deferred. Security configurations don't degrade over time because no one was watching.
In 2026, this kind of proactive posture is non-negotiable. Threat actors are faster than ever, and the window between a discovered vulnerability and active exploitation has narrowed to days — sometimes hours.
Best Practice 2: Strong Access Control and Identity Management
Access control is one of the most critical compliance requirements across all three industries — and one of the most frequently mismanaged.
IT support teams must ensure that users have access only to the information their role requires. Nothing more. This sounds simple, but in practice it requires real structure:
- Role-based access controls (RBAC) that are documented and reviewed regularly
- Regular access audits to catch permissions that have drifted out of alignment
- Immediate deprovisioning when an employee leaves or changes roles
- No shared accounts — every user needs individual accountability for audit trail purposes
- Multi-factor authentication (MFA) on all systems handling protected data
Access control policies should be living documents, not one-time setups. They need to be reviewed, tested, and updated as your organization grows, changes, or adds new systems.

Best Practice 3: Consistent Patch and Update Management
Unpatched systems remain one of the leading causes of data breaches and compliance failures in 2026. In regulated industries, missed updates don't just create security risk — they create regulatory exposure.
Best practice IT support follows a structured patch management process:
1. Updates are tested in a controlled environment
2. Scheduled deployments minimize operational disruption
3. Verification confirms updates applied successfully
4. Systems that can't be patched immediately are documented with compensating controls in place
That last point matters more than most people realize. Regulators and auditors don't expect perfection — they expect documentation and accountability. Knowing what you have, why it isn't patched, and what you're doing about it goes a long way in an audit.
Best Practice 4: Data Backup and Verified Recovery
Data loss in a regulated environment isn't just an operational problem — it's potentially a compliance violation. Under HIPAA, for example, you're required to maintain backup copies of electronic protected health information and have procedures to restore it.
Your backup strategy should include:
- Automated, frequent backups — not weekly, not manual
- Offsite or cloud-based copies that aren't connected to your primary systems
- Encrypted backups to protect data even if storage is compromised
- Regular restoration tests — because a backup you've never tested is just a hope
This last point is where many organizations fall short. Backing up data and actually being able to restore it are two different things. Your IT support team should be running verified recovery tests on a documented schedule.
Best Practice 5: Security Awareness Training
Technology controls only go so far. In 2026, phishing, social engineering, and credential theft remain the top attack vectors across all industries — and healthcare, education, and legal organizations are frequent targets because of the high value of their data.
Every person in your organization is part of your security posture. That means ongoing security awareness training — not a one-time annual checkbox, but regular, relevant education that keeps your team sharp:
- Simulated phishing exercises to test real-world response
- Clear protocols for reporting suspicious emails or activity
- Role-specific training for staff with elevated access or handling of sensitive data
- Regular reinforcement as new threats emerge
When your team knows what to look for, your risk profile drops significantly.
Best Practice 6: Documented Incident Response Plans
Every regulated organization needs a tested, documented incident response plan. Not a general outline — a specific, actionable plan that tells your team exactly what to do when something goes wrong.
Your plan should address:
- Detection and containment — how you identify and isolate a breach or failure
- Notification requirements — HIPAA breach notification has strict timelines (60 days for covered entities); FERPA has its own rules
- Communication protocols — who talks to regulators, clients, patients, or parents, and when
- Recovery steps — how you restore systems and verify integrity
- Post-incident review — what you document and how you improve
Having a plan on paper is a start. Testing it through tabletop exercises is what makes it real.
Best Practice 7: Vendor and Third-Party Risk Management
In regulated industries, your compliance obligations don't stop at your front door. If you share data with vendors, cloud providers, or third-party platforms, those relationships carry risk — and responsibility.
Under HIPAA, for example, vendors who handle protected health information must sign a Business Associate Agreement (BAA). In legal environments, data shared with outside services must be governed by appropriate confidentiality agreements.
Best practice IT support includes maintaining a current inventory of all third-party systems that touch your data, verifying their compliance posture, and reviewing those agreements regularly.
This is an area where managed IT services add significant value — a good partner tracks your vendor relationships and flags risk before it becomes a problem.
Why Managed IT Services Make Sense for Regulated Industries
Most healthcare practices, schools, and law firms don't have the internal resources to execute all of the above at the level these industries require. That's not a criticism — it's just reality. Compliance-grade IT support requires specialized knowledge, dedicated tooling, and consistent execution across every system, every day.
Managed IT services fill that gap. Deloitte's 2026 research on managed services highlights that the most effective models combine application maintenance and infrastructure management in an integrated operating model — with the speed and accountability of a single collaborator.
That's exactly what a strong managed IT partnership looks like in practice: one team, accountable for everything, with the expertise to keep you compliant and operational at the same time.
At AIS, we work with healthcare providers, educational institutions, and legal organizations across Las Vegas, Southern California, and surrounding regions. We bring 24/7 local support, dedicated account managers, and a 96% NPS score — because in regulated industries, the relationship matters as much as the technology.
Frequently Asked Questions
What does IT support in a regulated industry actually cover?
IT support in regulated industries covers everything from network monitoring and patch management to access control, data backup, incident response, and compliance documentation. It's a broader scope than standard IT support because the consequences of failure are higher — both operationally and legally.
How is HIPAA compliance different from general cybersecurity?
HIPAA compliance adds specific requirements on top of general cybersecurity best practices: audit trails for data access, breach notification timelines, Business Associate Agreements with vendors, and documented risk assessments. General cybersecurity is table stakes; HIPAA compliance is a structured framework layered on top.
Do small healthcare or legal organizations need managed IT services?
Yes — often more than larger ones. Smaller organizations typically have fewer internal IT resources but face the same regulatory requirements as large enterprises. A managed IT partner provides the expertise and infrastructure that would otherwise require a full internal team.
How often should access permissions be reviewed in a regulated environment?
At minimum, quarterly. But many compliance frameworks recommend reviewing access rights any time there's a personnel change — when someone is hired, changes roles, or leaves the organization. In practice, automated tools can flag permission drift in real time.

What happens if we fail a HIPAA or FERPA audit?
Consequences range depending on the severity and nature of the violation. HIPAA penalties in 2026 can reach millions of dollars in egregious cases, with tiered penalties based on culpability. FERPA violations can result in loss of federal funding. Beyond financial penalties, reputational damage and loss of patient or client trust are often the longer-lasting consequences.
What's the difference between a backup and a verified backup?
A backup is a copy of your data. A verified backup is a copy of your data that you've actually tested restoring. Many organizations discover during a real incident that their backups were incomplete, corrupted, or incompatible with their current systems. Regular restoration tests close that gap.
How do we evaluate a managed IT provider's experience with regulated industries?
Ask directly about their experience with your specific regulations (HIPAA, FERPA, etc.). Ask for examples of how they've helped clients pass audits or respond to incidents. Look for providers who can show you their documentation practices, not just describe them. And ask about their escalation process — regulated environments need clear accountability when something goes wrong.
Ready to Strengthen Your IT Support for Compliance?
If your organization operates in a regulated industry, the stakes are too high for reactive, inconsistent IT support. A structured, compliance-aware managed IT approach protects your data, your clients, and your reputation — while keeping your daily operations running without interruption.
Schedule a Free Consultation to talk through your compliance requirements and where your current IT support may have gaps.
Or reach out directly — Contact AIS Today and connect with a local expert who understands the demands of regulated industries.
Topics:
