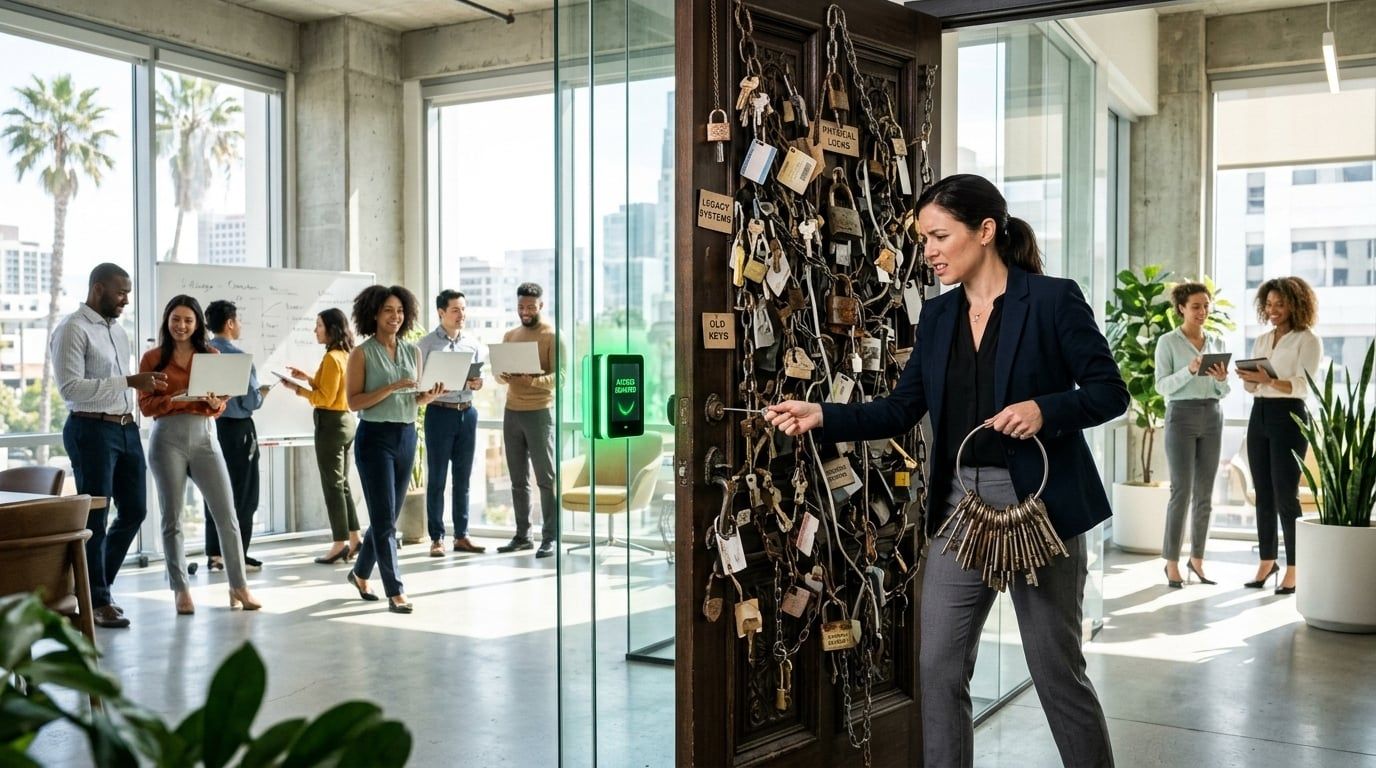
The main issues with legacy access control systems in Southern California include outdated hardware that lacks cloud connectivity, on-site servers that require costly manual maintenance, poor integration with modern identity management tools, and visibility gaps that leave organizations exposed to both physical and cyber threats. These systems were built for a different era of work and security.
Southern California businesses across Los Angeles, Orange County, San Diego, and the Inland Empire are upgrading away from these aging platforms. AIS provides security cameras and access control to offices throughout the region, helping organizations replace legacy systems with cloud-managed solutions that reduce risk and operational overhead.
What security system issues make legacy access control a liability for Southern California offices?
Legacy access control systems create security liabilities because they cannot integrate with modern threat detection tools, run on unpatched operating systems, and rely on physical credentials like key cards that are easy to clone or lose. According to the Ponemon Institute, only 44% of organizations reported being highly confident in their ability to prevent identity-based security incidents, reflecting how widespread access visibility gaps have become.
How do legacy security system issues expose Southern California offices to breaches?
Older systems typically run on isolated, on-premise servers that receive little to no software updates. These servers become easy targets for attackers once they gain network access, since the firmware and operating systems often contain known vulnerabilities that vendors no longer patch.
Why do legacy access control problems make credential management harder?
Legacy systems rely on magnetic stripe or older proximity cards that offer minimal encryption. These credentials can be duplicated with inexpensive equipment, making it straightforward for an unauthorized person to gain building access without triggering any alert.
Why are on-site servers a core legacy access control problem for Southern California businesses?
On-site servers are a core legacy access control problem because they require dedicated IT staff or vendor visits for maintenance, create single points of failure, and cannot scale easily across multiple office locations. As Security Info Watch reports, organizations are actively migrating toward cloud-managed platforms to reduce the operational overhead that on-premises infrastructure demands.
What maintenance burdens do legacy security systems create for Southern California offices?
Every firmware update, software patch, and hardware replacement requires either an in-house technician or a scheduled vendor visit. For multi-site businesses across Southern California, this creates compounding costs and downtime across each location.

How do on-site legacy access control systems affect business continuity?
If the on-site server fails, the entire access control system for that building may go offline. Cloud-managed replacements distribute system functions across redundant infrastructure, so a single hardware failure does not lock employees out or disable logging.
What are the legacy access control problems related to remote management in Southern California offices?
Legacy access control systems typically cannot be managed remotely without a VPN, and VPN-dependent management adds latency, security risk, and complexity. Southern California businesses with hybrid or distributed workforces find these constraints particularly costly because IT and security teams cannot quickly grant, modify, or revoke access credentials without being physically present or logging into fragile VPN tunnels.
How do legacy security system issues slow down user provisioning for Southern California teams?
Adding or removing an employee's building access on a legacy system often requires manual database entries through a local workstation. This process can take hours or days, creating windows where former employees retain active credentials after separation.
Why does VPN dependency make legacy access control problems worse for Southern California offices?
VPNs introduce additional attack surface and require maintenance of their own. When a VPN is misconfigured or compromised, the access control system it protects becomes reachable from outside the network perimeter, which significantly elevates breach risk.
How do legacy access control problems create compliance risks for Southern California businesses?
Legacy systems often lack audit logging, role-based access controls, and reporting features required by regulations such as HIPAA, CMMC, and California's own CCPA framework. Without these capabilities, Southern California offices in healthcare, legal, defense contracting, and financial services face audit failures, fines, and potential contract losses.
What specific security system issues affect compliance reporting in Southern California offices?
Modern compliance frameworks require organizations to demonstrate who accessed what, when, and from where. Legacy systems frequently store incomplete logs or overwrite them on a short cycle, making it impossible to produce the evidence an auditor or regulator requires.
How do legacy access control problems intersect with California-specific security regulations?
California maintains some of the strictest data privacy and security regulations in the country, including the California Consumer Privacy Act and industry-specific requirements enforced by state agencies. Legacy systems that cannot produce detailed access logs or enforce least-privilege policies put businesses out of compliance by design, not by accident.
What is the cost of keeping legacy access control systems in a Southern California office?
The total cost of maintaining legacy access control in a Southern California office includes hardware replacement parts, on-site technician labor, VPN licensing, and the hidden cost of security incidents caused by system gaps. Organizations that delay modernization often find that a single security event, whether a breach or a compliance fine, costs more than a full system replacement would have.
How do legacy security system issues drive up IT costs for Southern California businesses?
Older systems require proprietary replacement parts that become harder to source as manufacturers discontinue product lines. When components fail, emergency procurement and after-hours technician visits carry premium pricing that compounds over time.
What is the ROI case for replacing legacy access control problems with cloud-managed systems?
Cloud-managed access control eliminates on-site server costs, reduces technician visits, enables remote administration, and integrates with identity platforms like Microsoft Azure Active Directory. For a Southern California office managing 50 or more employees across multiple floors or buildings, the operational savings typically offset migration costs within 12 to 24 months.
FAQs
What are the most common legacy access control problems in Southern California offices?
The most common problems include outdated on-site servers, unencrypted key card credentials, no remote management capability, and missing audit logs required for regulatory compliance. These issues affect businesses across every industry in the Southern California region.
How do security system issues in legacy access control increase cyber risk?
Legacy systems often run unsupported operating systems and lack integration with modern security information and event management platforms, leaving physical access events invisible to cybersecurity teams. This creates blind spots that attackers can exploit to move laterally through a network after gaining physical access.
Can Southern California offices integrate legacy access control systems with modern software?
Some legacy systems support partial integration through middleware, but these workarounds are fragile and typically cannot deliver the real-time data and automation that modern identity management platforms require. Full replacement is usually the more reliable and cost-effective path.

How long does it take to replace a legacy access control system in a Southern California office?
Replacement timelines vary by building size and system complexity, but most mid-size Southern California offices complete a full migration to a cloud-managed access control platform within 30 to 90 days. Planning and credential migration typically take the most time.
What should Southern California businesses look for when replacing a legacy access control system?
Prioritize cloud-native management, mobile credential support, role-based access controls, real-time audit logging, and integration with your existing identity provider. These features address the core legacy access control problems while positioning your office for future security needs.
The Bottom Line on Legacy Access Control Problems for Southern California Offices
Legacy access control systems expose Southern California offices to preventable security incidents, rising maintenance costs, and compliance failures that cloud-managed alternatives are built to eliminate. The Ponemon Institute's finding that fewer than half of organizations feel confident in preventing identity-based incidents reflects how urgently businesses need to close these gaps.
Replacing an aging system is a straightforward investment when measured against the cost of a breach or a failed audit. Connect with an AIS technology advisor to review your current access control setup and get a clear plan for modernizing your Southern California office security.
Topics:
