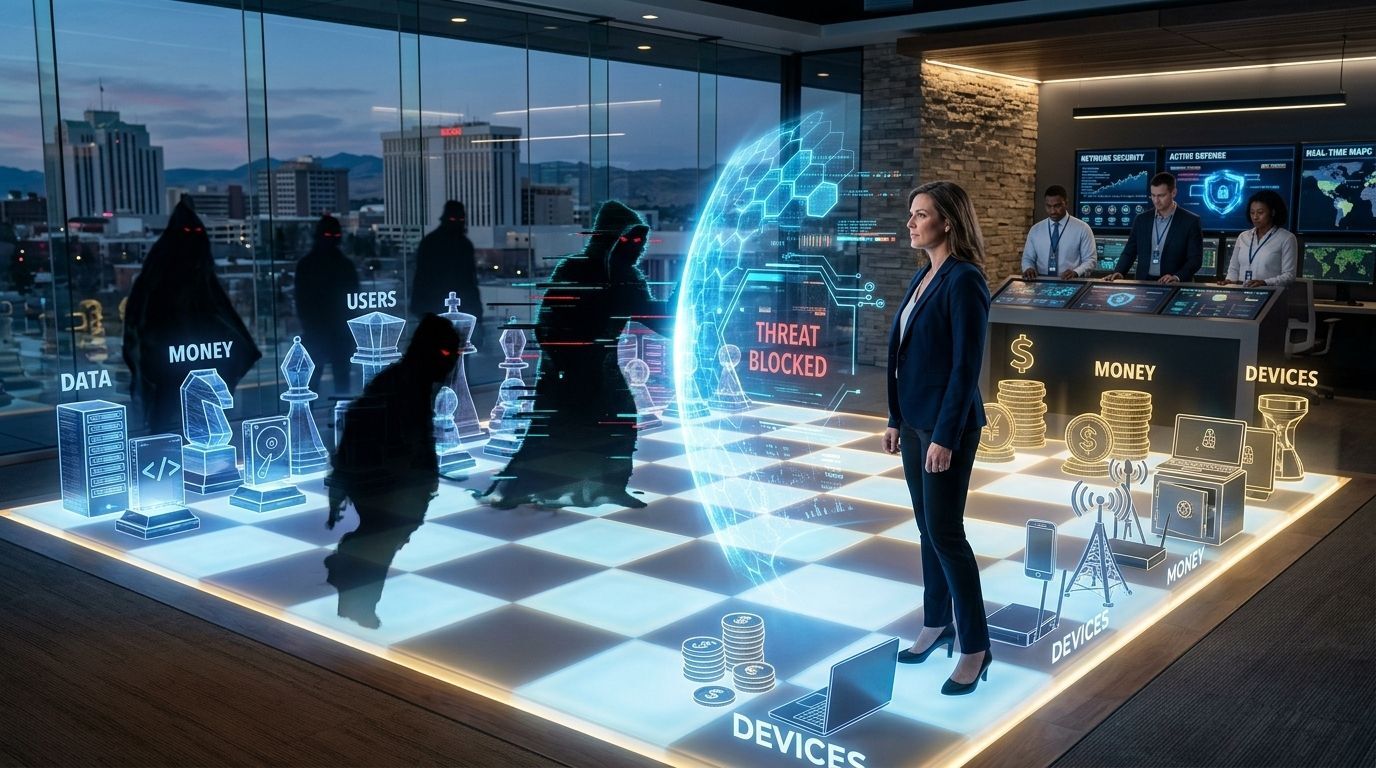
Managed IT services reduce cybersecurity risks for Nevada SMBs by providing continuous network monitoring, automated patch management, threat detection, and rapid incident response. These services replace the need for a full in-house security team and apply enterprise-grade protection at a price point accessible to small and mid-sized businesses. The result is fewer vulnerabilities, faster response times, and measurable risk reduction.
AIS provides managed IT services to SMBs across Nevada and Southern California, giving local businesses access to a full security stack without the overhead of internal IT staff. From Las Vegas to Henderson, AIS helps teams stay protected against modern threats.
What cybersecurity risks do Nevada SMBs face most often?
Nevada SMBs face phishing attacks, ransomware, credential theft, and data breaches at increasing rates. Small businesses are frequently targeted because attackers assume they lack dedicated security resources. Industries like hospitality, construction, legal, and healthcare in Nevada face added risk because they handle sensitive financial and personal data.
Why are cybersecurity threats growing for Nevada SMBs?
Cybercriminals increasingly target small businesses because they often use outdated software, weak password policies, and unmonitored networks. According to IDC's December 2025 report, 57% of U.S. SMBs listed increased security as a top infrastructure priority for the next 12 months, signaling widespread recognition of this growing threat. Nevada's tourism and gaming economy creates additional exposure through high-volume payment processing and sensitive customer records.
What industries in Nevada face the highest IT service security risks?
Hospitality, legal, and medical businesses in Nevada carry the highest cybersecurity risk because of the volume and sensitivity of the data they store. A single breach in these sectors can trigger regulatory fines, client loss, and reputational damage. Managed IT security specifically addresses these industry-level risks through tailored compliance monitoring and data protection controls.
How does 24/7 monitoring reduce cybersecurity risks for Nevada SMBs?
Continuous 24/7 monitoring reduces cybersecurity risk by detecting threats in real time, before attackers can move laterally through a network or exfiltrate data. Most cyberattacks happen outside business hours, when internal staff are unavailable. A managed IT provider watches your environment around the clock and responds to alerts immediately, cutting breach windows from days to minutes.

What does real-time threat detection mean for IT service security?
Real-time threat detection means your managed IT provider uses automated tools and human analysts to identify suspicious activity the moment it occurs. Systems flag abnormal login attempts, unusual data transfers, and unauthorized software installations instantly. This speed is critical, since the average time to detect a breach without active monitoring can exceed 200 days, according to industry data from IBM (https://www.ibm.com).
How does managed IT monitoring specifically protect Nevada SMB networks?
Managed providers deploy Security Information and Event Management (SIEM) tools that aggregate logs from every endpoint, firewall, and application in your network. These tools correlate events across your environment to identify attack patterns that individual alerts would miss. For Nevada SMBs with remote employees or multiple locations, centralized monitoring through a managed service is often the only practical way to maintain full visibility.
What specific IT service security controls do managed IT providers deliver?
Managed IT providers deliver a layered security stack that includes endpoint protection, firewall management, email filtering, multi-factor authentication enforcement, vulnerability scanning, and patch management. These controls work together to reduce the attack surface of your business. No single tool eliminates risk, but this combined approach addresses the most common threat vectors SMBs encounter.
Why is patch management a critical part of cybersecurity for Nevada SMBs?
Patch management is the process of regularly updating software, operating systems, and firmware to close known security vulnerabilities. Attackers routinely exploit unpatched systems, and many SMBs fall months behind on updates due to limited IT resources. A managed IT provider automates this process and ensures your systems stay current without disrupting daily operations.
How does multi-factor authentication reduce IT service security risks?
Multi-factor authentication (MFA) requires users to verify their identity through two or more methods before accessing systems or data. This single control blocks the majority of credential-based attacks, including phishing and password spray attempts. Managed IT providers configure, enforce, and monitor MFA across all business accounts, including Microsoft 365, cloud applications, and remote access tools.
How do managed IT services help Nevada SMBs meet compliance requirements?
Managed IT services help Nevada SMBs meet compliance requirements by aligning security controls with frameworks like HIPAA, PCI-DSS, and CMMC. Providers document policies, run vulnerability assessments, and generate audit-ready reports that demonstrate regulatory adherence. This reduces the legal and financial exposure that comes with a compliance failure or data breach.
Which Nevada SMB industries require specific cybersecurity compliance standards?
Medical practices must meet HIPAA requirements for protecting patient health information. Businesses that accept credit or debit card payments must comply with PCI-DSS standards. Law firms and government contractors in Nevada may also face CMMC or state-level data privacy requirements under Nevada Revised Statutes Chapter 603A.
How does a managed IT provider reduce the cost of compliance for small businesses?
Compliance without a managed provider typically requires hiring specialized staff, purchasing separate compliance tools, and conducting costly third-party audits. A managed IT partner bundles compliance monitoring, documentation, and reporting into a predictable monthly cost. According to Deloitte's Future of Cyber Survey 2024, 90% of U.S. cybersecurity decision-makers expect their increased security activities to achieve desired business outcomes to a moderate or large extent, reinforcing that structured investment in security and compliance delivers measurable returns (https://www.deloitte.com/us/en/services/consulting/articles/future-of-cyber-survey-2024.html).
What should Nevada SMBs look for in a managed IT security partner?
Nevada SMBs should look for a managed IT security partner that offers 24/7 monitoring, a documented incident response plan, compliance expertise relevant to their industry, and transparent monthly pricing. Local presence matters because a provider familiar with Nevada's business environment can respond on-site when needed. Experience with businesses of similar size ensures the tools and processes fit your actual needs.
How does risk reduction differ between a local and national managed IT provider for Nevada SMBs?
A local managed IT provider in Nevada can offer faster on-site response, familiarity with regional compliance requirements, and direct relationships with your team. National providers may offer broader toolsets but sometimes lack the responsiveness and local context that SMBs need. For most Nevada SMBs, a local or regional provider delivers more practical cybersecurity value day to day.
What questions should Nevada SMBs ask before signing a managed IT services agreement?
Before signing, ask about average response times for critical incidents, whether security monitoring is included or costs extra, and how the provider handles a confirmed breach. Ask for documentation of their own security practices and certifications such as SOC 2 or ISO 27001. You should also confirm that your IT support agreement includes regular security reviews and not just reactive helpdesk services.
FAQs
How much does managed IT security cost for cybersecurity Nevada SMBs?
Managed IT services with cybersecurity for Nevada SMBs typically cost between $75 and $150 per user per month. A 15-person business can expect to pay roughly $1,125 to $2,250 monthly, depending on the depth of security monitoring and compliance support included.
Can managed IT services fully prevent cyberattacks for Nevada small businesses?
No managed IT service can guarantee zero attacks, but the right provider significantly reduces the likelihood and impact of a breach. Continuous monitoring, patching, and endpoint protection dramatically shrink your attack surface and accelerate containment when an incident does occur.

What is the difference between IT service security and traditional antivirus software?
Traditional antivirus software reacts to known threats using signature-based detection, while IT service security from a managed provider uses behavioral analysis, SIEM tools, and human oversight to catch both known and unknown threats. Managed security is proactive; antivirus alone is not sufficient for business-grade protection.
How quickly can a managed IT provider respond to a cybersecurity incident in Nevada?
Most managed IT providers offer response time SLAs ranging from 15 minutes to 4 hours for critical incidents, depending on the service tier. Providers with a local Nevada presence can also dispatch on-site technicians when remote remediation is not enough.
Do managed IT services help with employee cybersecurity training for Nevada SMBs?
Many managed IT providers include security awareness training as part of their service package or offer it as an add-on. This training teaches employees to recognize phishing emails, avoid unsafe links, and follow secure password practices, addressing the human element that accounts for the majority of successful breaches.
The Bottom Line on Cybersecurity for Nevada SMBs
Managed IT services give Nevada SMBs access to enterprise-grade cybersecurity tools, 24/7 monitoring, compliance support, and rapid incident response without the cost of building an internal security team. With 57% of U.S. SMBs prioritizing increased security in 2025 according to IDC, the shift toward managed protection is not optional for businesses that want to stay competitive and resilient. The businesses that act now reduce both their risk exposure and their long-term recovery costs.
Ready to build a stronger security posture for your Nevada business? Talk to an AIS technology advisor to find out which managed IT security services fit your size, industry, and budget.
Topics:
